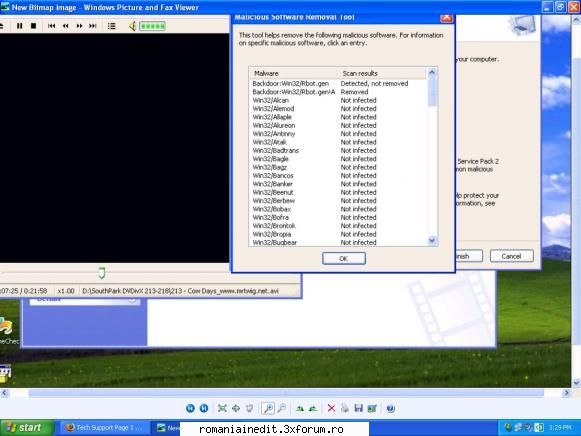
Backdoor.Rbot is a family of Trojan programs for Windows, which offer the user remote access to victim machines. The Trojans are controlled via IRC, and have the following functions:
* monitor networks for interesting data packets (i.e. those containing passwords to FTP servers, and e-payment systems such as PayPal etc.) * scan networks for machines which have unpatched common vulnerabilties (RPC DCOM, UPnP, WebDAV and others); for machines infected by Trojan programs (Backdoor.Optix, Backdoor.NetDevil, Backdoor.SubSeven and others) and by the Trojan components of worms (I-Worm.Mydoom, I-Worm.Bagle); for machines with weak system passwords * conduct DoS attacks * launch SOCKS and HTTP servers on infected machines * send the user of the program detailed information about the victim machine, including passwords to a range of computer games
Evident , scapi de el cu Kaspersky
_______________________________________ Zilnic, cel mai interesant P.M. este răsplătit cu un BONUS special DO NOT PM ME, MOST LIKELY I WON'T ANSWER.DO NOT REQUEST REUPLOADS OF MY PREVIOUS UPLOADS, BUT IF YOU STILL HAVE THEM, FEEL FREE TO MAKE AS MANY MIRRORS AS YOU LIKE. [mp3=https://www.youtube.com/watch?v=azJTTI4vk7g]